

FIELD NOTE · CISSP DOMAIN 2: ASSET SECURITY
Asset handling | Physical access | Insider risk
Opening Scene
I remember it like it was yesterday.
A younger Amber walked into the office one morning, greeted my colleagues, and headed toward my desk. I put down my bag and settled into my chair, ready to begin another day supporting the company’s executives.
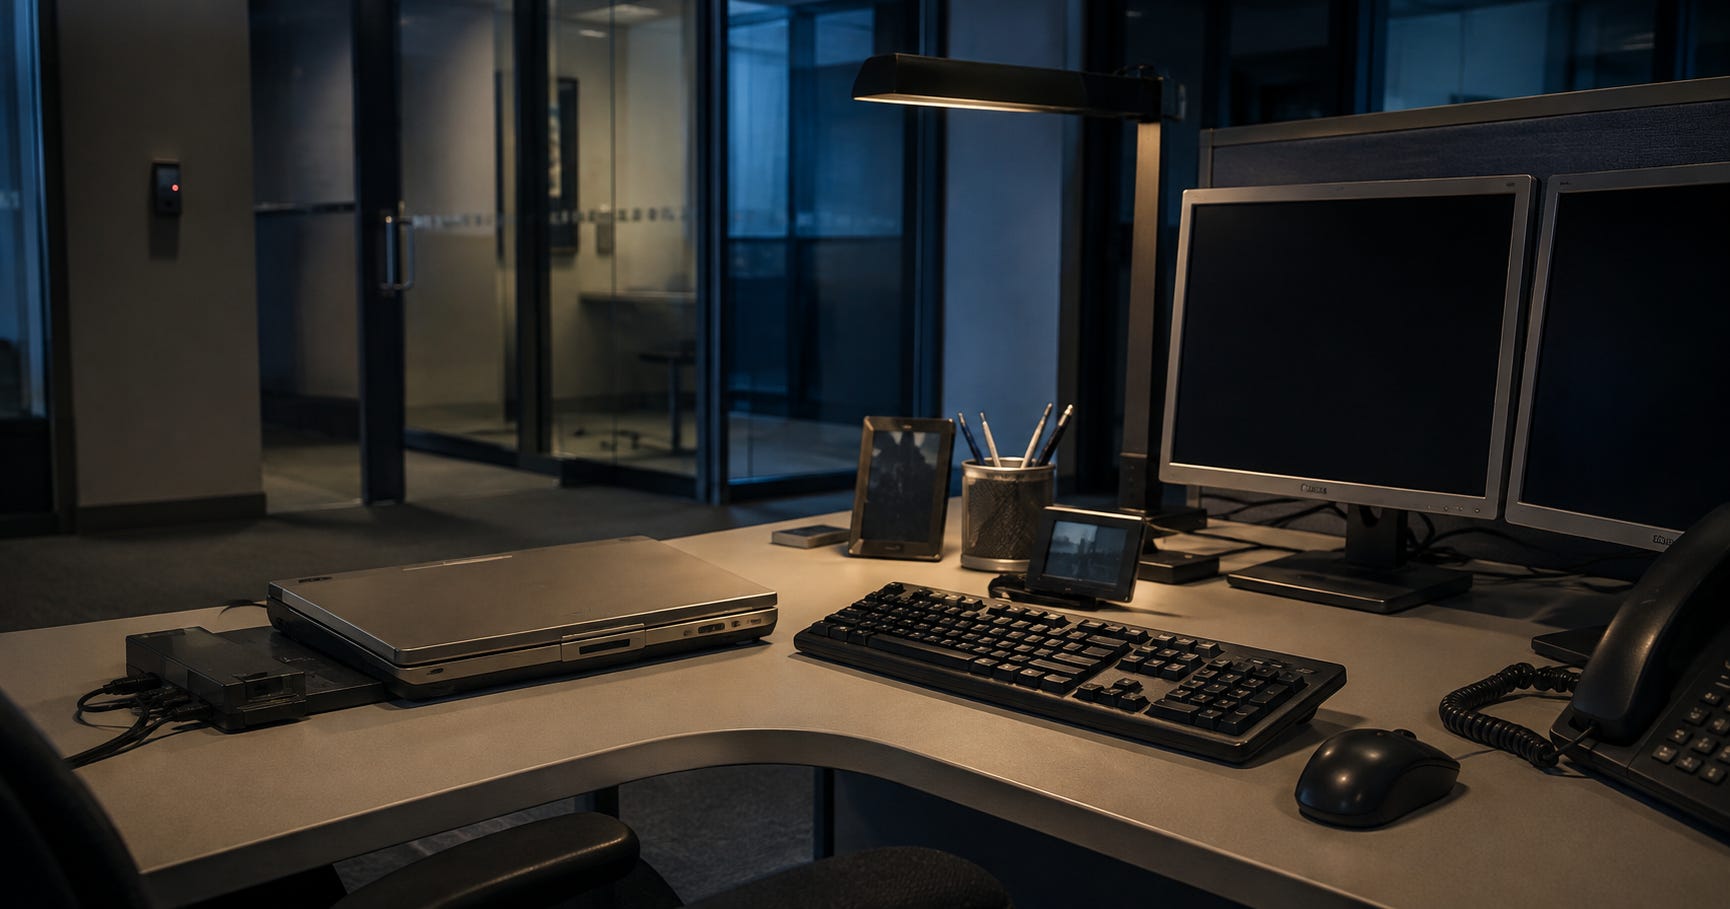
My keyboard was there. So were my docking station, mouse, desk phone, and photos.
Something was missing.
My laptop.
I knew I had left it on my desk the night before. I did not have any work to finish at home, so I had not taken it with me. But now it was gone.
I searched around the office and checked with my coworkers. Had I carried it to someone else’s desk while we were saying goodbye? Were they playing a prank on me?
No one knew anything about my missing laptop.
After searching everywhere I could think of, fear began to settle in. I was going to have to tell my boss that I could not account for a company laptop.
What kind of trouble was I in? What information was stored on that laptop? And if someone could access it, what could this mean for the organization?
What Happened?
I sat at my desk wondering how I was going to tell my boss that my laptop was missing. How would I help the executives if they had computer or network problems? I could not even access my support tickets.
While I waited for my boss to arrive, I went to the C-suite and checked with the executive assistants to see whether anyone needed help.
The entire time, I was avoiding the conversation I knew I needed to have.
When I returned to my floor, my boss had arrived.
I slowly walked into her office and asked whether she had a moment to talk. She welcomed me in with an expectant look on her face. I stumbled over my words before finally mustering the courage to tell her that I did not know where my laptop was.
I explained that I had left it on my desk and why I had not taken it home because I did not have any work to complete that evening. At the time, leaving it inside the office had seemed reasonable.
She listened as I explained myself for what felt like five minutes. Then she reached into her desk drawer, pulled out a laptop, and placed it on her desk.
“Is this what you’ve been looking for?” she asked. “I was wondering how long it would take you to tell me you didn’t have it.”
My heart sank.
I had spent the morning searching the office, questioning my coworkers, and imagining the consequences of losing a company laptop. Now I learned that my boss had taken it from my desk and waited for me to report it missing.
At the time, I felt hurt. It seemed as though she had watched me panic to teach me a lesson. I was also embarrassed.
She explained the risks of leaving a company laptop unattended overnight and told me this was my warning not to do it again.
I left her office feeling unprofessional and ashamed that I had not taken the security of a company asset seriously. Until that morning, I believed the laptop was safe because it was behind secured office doors.
I had not considered that employees, contractors, or even my peers already had access to the building and could have taken it if they had ill intentions.
I had treated the secured office as though it eliminated the risk.
Clearly, my boss believed otherwise.
What Was Really Going On?
More than 20 years later, I cannot say that no one explained the company’s laptop policy to me. I likely reviewed it during onboarding and received guidance about handling company equipment.
What I cannot remember is whether I failed to understand its importance or understood the policy and decided that leaving my laptop behind secured office doors was safe enough.
What I know is that I made a judgment call based on an incomplete view of the risk.
At the time, I treated the office boundary as the security boundary. The doors required authorized access, so I assumed anything left behind them was protected.
Those doors reduced the risk, but they did not eliminate it.
People with legitimate access to the building could still reach my desk. I had not considered the possibility of an insider threat or someone misusing the access they had been given.
My boss demonstrated the weakness in my assumption. She had legitimate access to the office, removed the laptop from my desk, and kept it without my knowledge.
This experience connects most directly to Certified Information Systems Security Professional (CISSP®) Domain 2: Asset Security. The laptop belonged to the company, but as its assigned user, I was responsible for handling it according to the organization’s requirements and maintaining appropriate custody of it.
A secured building was one layer of protection. It did not relieve me of that responsibility.
The lesson was not simply that I should have taken the laptop home. Carrying a company computer outside the office would have introduced a different set of risks.
There was another problem. Once I realized the laptop was missing, I delayed reporting it.
I was afraid of getting in trouble, so I spent valuable time trying to solve the problem quietly. Had the laptop actually been stolen, that delay could have limited the organization’s ability to respond quickly, protect its information, and determine whether its information had been exposed.
If I could return to that desk in 2005, I would handle the situation differently.
What I Would Do Differently
Knowing what I know now, I would make several different decisions. Some involve how I handled the laptop before leaving the office. Others concern how I responded once I realized it was missing.
Confirm the policy instead of guessing
I would verify whether the laptop needed to come home with me, be placed in a locked drawer, or be stored another approved way. I would not assume that leaving it behind secured doors was enough.
Secure the laptop appropriately
I would not leave it sitting visibly on my desk overnight where anyone with access to the office could take it.
Consider who actually has access
A badge reader may keep out many unauthorized people. It does not eliminate the risk posed by employees, contractors, cleaning personnel, vendors, or someone misusing legitimate access.
Authorized access and trustworthy behavior are not the same thing.
Protect the information, not just the hardware
I would ask what information was stored on the hard drive, whether it was encrypted, what systems the laptop could access, and how quickly those connections could be disabled.
Losing the device would matter. Exposing the information or access associated with it could create a much larger consequence for the organization.
Report the issue immediately
I would not spend the morning quietly searching and hoping the laptop would turn up. I would contact my manager and the appropriate IT or security team as soon as I noticed it was missing.
Embarrassment should never delay the organization’s ability to respond.
Turn the experience into a lesson learned
My Project Management Professional (PMP®) experience has taught me that lessons should not remain isolated memories. We capture them so they can improve future decisions, strengthen processes, and help others avoid repeating the same mistake.
This became one of my earliest personal lessons learned: when something involving a company asset does not look right, report it immediately.
Create the conditions for people to speak up
I understand why my boss wanted me to recognize the seriousness of what I had done. The lesson stayed with me. Still, as a leader, I would not knowingly allow someone to panic while waiting to see how long it took them to speak up.
What I learned through becoming a Certified ScrumMaster® (CSM) reinforced the importance of transparency, openness, respect, and the courage to raise problems early. I would address the behavior directly, explain the risk, and ask what could be improved to prevent it from happening again.
Accountability would still matter. So would creating an environment where people are willing to tell the truth quickly.
When people are afraid to report mistakes, the organization may learn about its risks too late.
Closing Reflection
For years, I remembered this as the morning I got in trouble for leaving my laptop at work.
Now I recognize it as one of my earliest lessons in security judgment.
The secured doors had not failed. They limited who could enter the office, but they could not control what every authorized person might do once inside. My mistake was not recognizing the boundary of that protection. I treated one functioning control as though it eliminated the risk.
It did not.
The experience also taught me that reading a policy is not the same as understanding the risk behind it. Organizations can document expectations, but employees still have to connect those requirements to the decisions they make every day.
Leaders also have a responsibility to create an environment where people understand why a policy matters and feel able to speak up when something goes wrong.
That connection is where security awareness becomes security judgment.
This lesson still influences how I approach identity and access management, program leadership, and team accountability. Granting someone access does not guarantee how that access will be used. A badge, password, role, or policy is only one part of the protection around an asset.
I no longer ask only whether a control exists.
I also ask what it protects, what it does not protect, and what responsibility remains with the person trusted to use it.
This is only one of the early-career lessons that shaped how I lead security programs today. In the weeks ahead, I will share more of those experiences: what happened, what I learned, and how those lessons connect to the work we do in project management, agile delivery, identity, and security.
The challenge is rarely the absence of a framework.
The difficult part is what happens when the framework meets people.
Reader Question
What lesson from early in your career still influences how you work today?
Filed under: Field Notes
Professional lenses: CISSP® Domain 2: Asset Security; PMP®: Lessons Learned; Certified ScrumMaster® (CSM): Transparency, Openness, and Continuous Improvement
Topics: Asset Security, Authorized Access, Incident Reporting
The Dovia Brief shares real-world lessons from enterprise identity, security, and program leadership. Published by Tech Dovia.